

client_id and client_secret) and pilot how Finch works in a safe testing environment with mock data.
- Go to the Finch Developer Dashboard and sign up for a new account. You’ll need to provide your name, company name, email address, and create a password.
- Once you have created an account and logged in, locate the sandbox application in the upper left which was automatically created.
- Upon creating the application, you’ll be provided with a
client_idandclient_secret. You will use these credentials to authenticate your application to obtain access tokens in order to call the Finch APIs. - Set up a secure method for storing your
client_id,client_secret, and futureaccess_tokens to prevent unauthorized access. Here are some methods to securely store these credentials:- Environment Variables: Store your
client_idandclient_secretas environment variables within your application. When your application needs to use these credentials, it can access them from the environment variables without exposing them in your source code. - Secure Database: Store the access tokens in a secure database with proper encryption and access controls in place. Make sure to use a database that supports encryption at rest and in transit to ensure the security of the stored tokens.
- Secrets Management Solutions: Utilize a specialized secrets management solution, such as HashiCorp Vault or AWS Secrets Manager. These tools provide additional layers of security, access control, and auditing capabilities to ensure the safe storage of your
client_id,client_secret, andaccess_token. - When storing access tokens, also store any relevant metadata, such as the associated employer ID. This will help you maintain data integrity and prevent mixing up tokens across different employers. This topic is covered in more detail in Store Tokens.
- Environment Variables: Store your
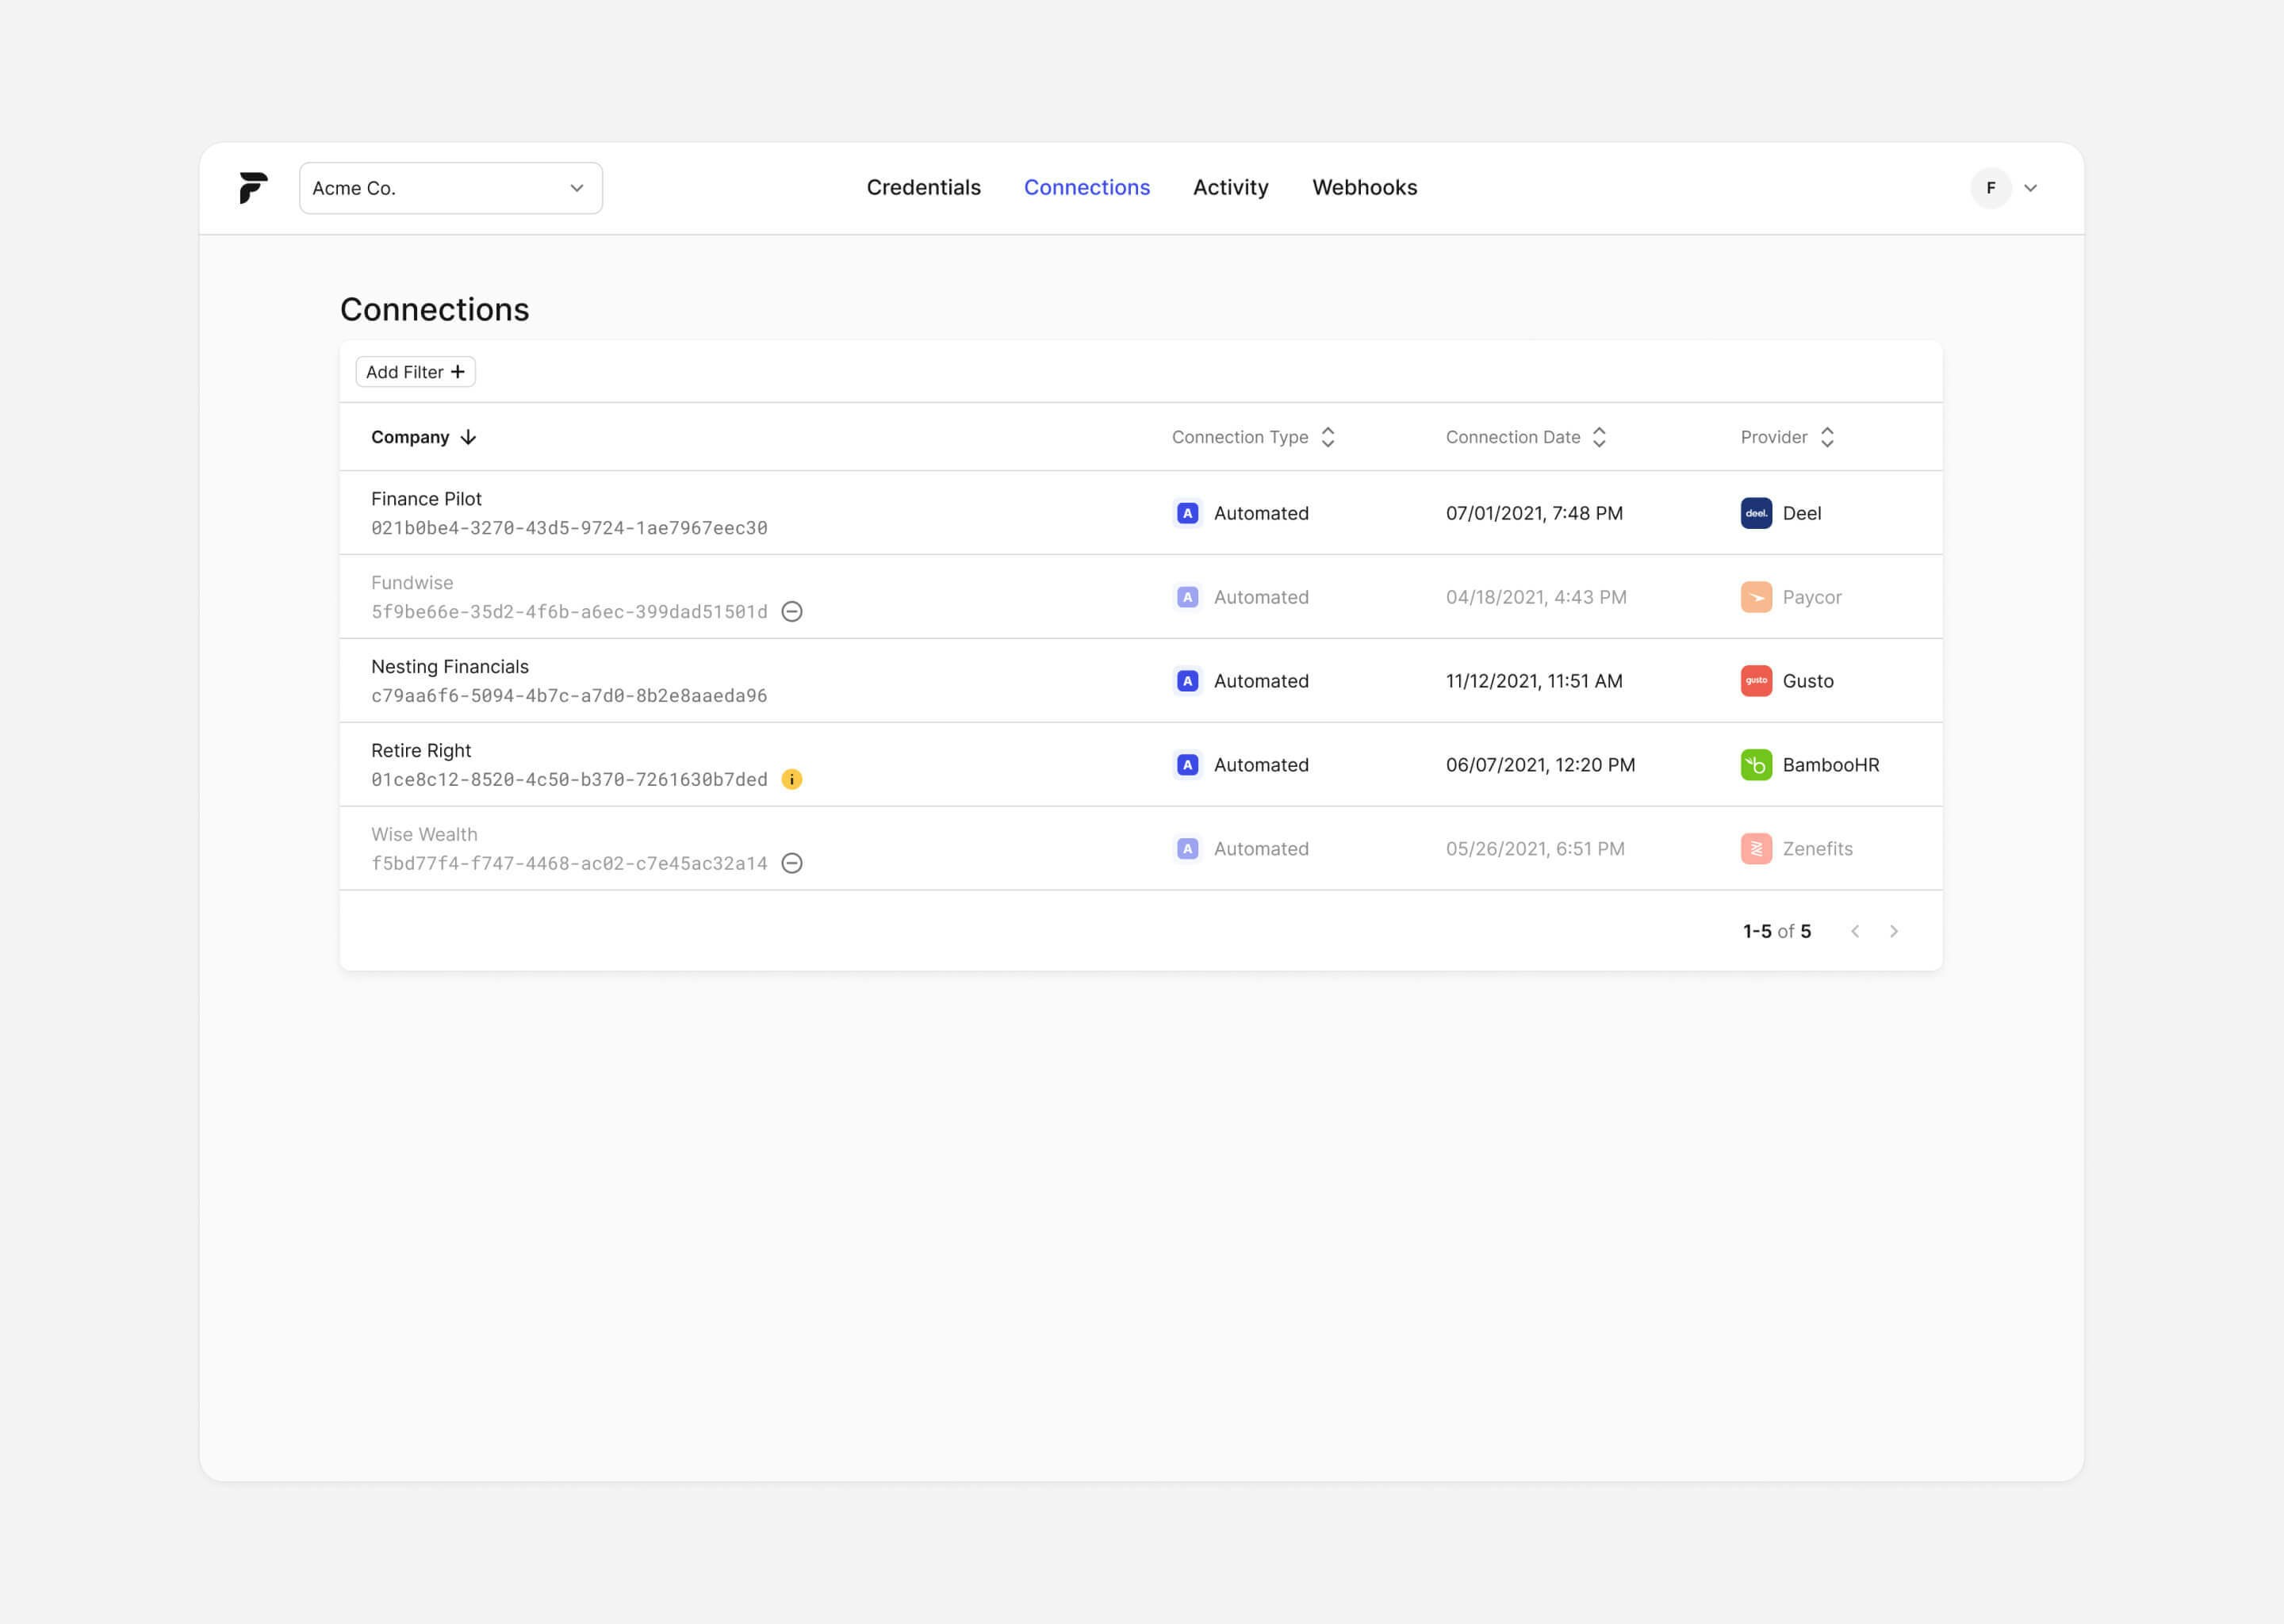
Familiarize Yourself With the Finch Developer Dashboard
The Finch Developer Dashboard is your centralized place to manage your Finch Applications, view current connections, review request activity, and set up webhook alerts. We will cover these tabs in more detail in the following sections, but here is a quick overview.- Credentials: View your application credentials, including your
client_idandclient_secret, and product scopes. - Connections: View the status of your connections, including the last sync time and any errors that occurred.
- Integrations: Manage providers that you have integrated with, including the ability to enable or disable specific providers.
- Activity: Review the activity log to see a history of requests made by your application, including the request type, status, and timestamp.
- Webhooks: Set up webhook alerts to receive notifications when specific events occur, such as a connection error or a successful sync.
Verify Product Scopes
On the Credentials tab, verify the correct products (commonly called “scopes”) are checked that your application will need access to. Products determine the specific data your application can access and the actions it can perform. Each product refers directly to a Finch endpoint. If the products are not correct, reach out to your Implementation Engineer or developers@tryfinch.com.Add Redirect URIs
When using the Finch Connect Redirect Flow, register one or more Redirect URIs for your application. Redirect flow requires at least one registered URI; embedded flow does not require a registered URI. Each URI must be hosted on your own server or a trusted domain. Example:https://your-trusted-domain.com/api/finch/callback
Registering a redirect URI tells Finch where it may send authorization codes for your application, so codes only reach URLs you control. In the redirect flow, pass one of your registered URIs as redirect_uri in two requests:
- When creating the Finch Connect session —
POST /connect/sessions, orPOST /connect/sessions/reauthenticatefor reauthentication. Finch returns a400if the URI isn’t registered. After the employer authorizes your application, Finch redirects them to this URI with an authorizationcodequery parameter. - When exchanging the code for an access token —
POST /auth/token. Theredirect_urimust match the one used to create the session, or Finch returns a400invalid_grant_error. See Retrieve Access Token.
https://tryfinch.com is already applied.
The redirect URIs must match one of the following formats—
Checkpoint + Next Step
After completing this step, you should have registered for a Finch Developer Dashboard account and set up a sandbox application, using your unique
client_id and client_secret. You should also have a clear understanding of the Finch products that your application requires. You now have everything necessary to Integrate Finch Connect Into Your Application to begin connecting to employment providers.